VMRay Labs Note. By Emre Güler, VMRay Labs. 01.09.2026.
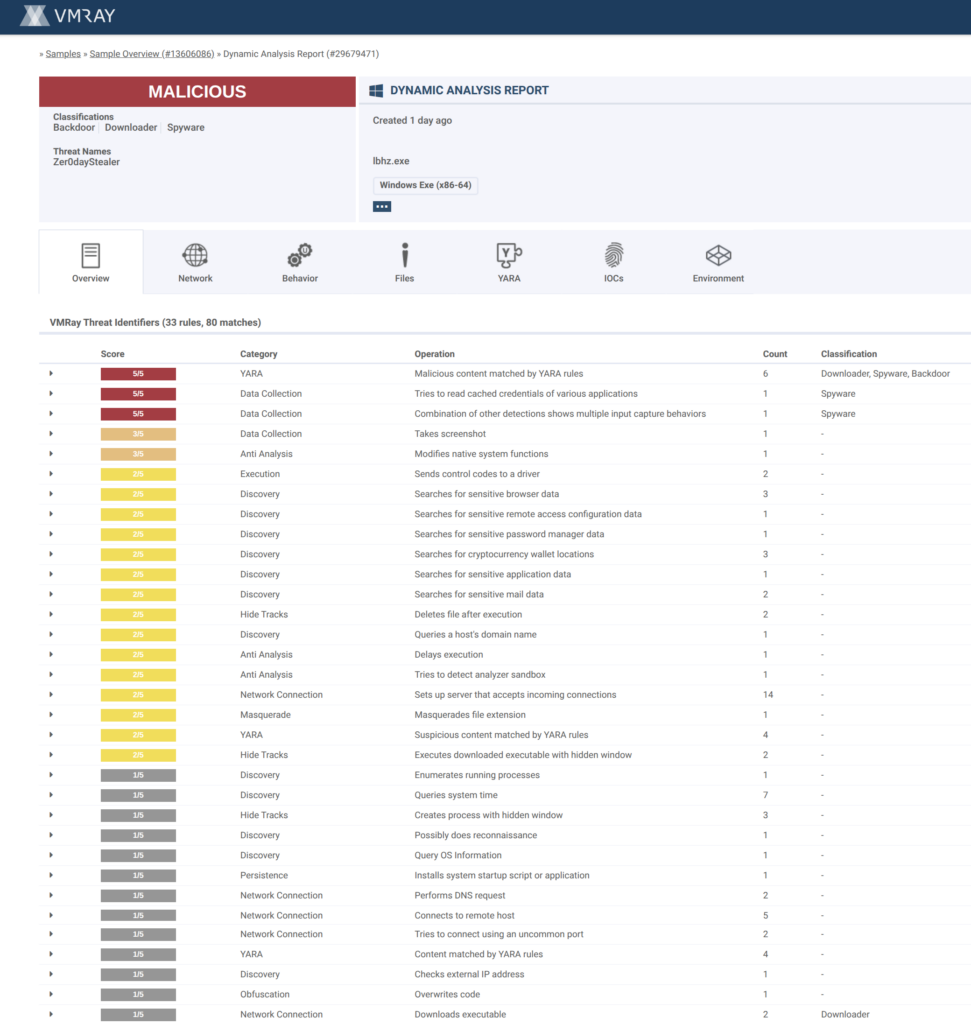
Key finding. A single artifact left in a binary during compilation, a developer’s home directory path, connected a Rust-based infostealer that VMRay Labs calls “Zer0day Stealer” to a separate HVNC remote-control tool and to a recently reported ransomware family, ENIGMA Locker. Searching for that one string surfaced earlier versions of the stealer, multiple droppers, and a wider cross-platform malware operation, a reminder that the small artifacts a build process leaves behind can undo an operator’s anonymity.

What was observed
Zer0day Stealer is written in Rust and carries a build path, /home/tcherber/.cargo/, baked into the binary. That path is the thread. A search for it turned up earlier versions of the stealer and, more tellingly, an unrelated ransomware family, ENIGMA Locker, carrying the same path. The same developer is also the likely author of an HVNC remote-control sample often deployed alongside the stealer: it shares the home path and was compiled within seconds of related samples. Across the set, compilation timestamps showed everything was built within a span of a few weeks.
The search also surfaced the surrounding toolkit: a dropper written in C, another in Rust, and a PowerShell loader that abuses the legitimate certutil utility, all of which deliver a variant of the same stealer and HVNC pair.
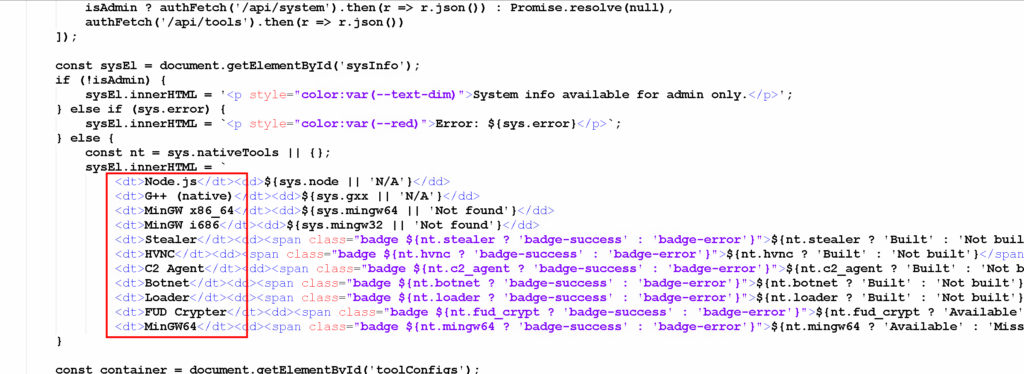
A few details stand out. The stealer exfiltrates crypto wallets and browser credentials, and newer versions show active development, from changed C2 addresses to file-extension-based theft targeting Office documents and VPN configuration files. The HVNC sample ships with a hardcoded password and uses a single-byte patch to evade AMSI and ETW, the Windows interfaces security tools rely on to inspect activity. One dropper variant shows the build path changed to /root/.cargo, suggesting the developer moved to a different machine. And the C2 interface leaked further evidence of cross-platform builds for Windows, Linux, and macOS, alongside other tools labelled “FUD-Crypter,” “Botnet,” and “C2 Agent.”

Why it matters
The theft capability is ordinary. The lesson is in how the operation was mapped. Strings like build paths, PDB filenames, and other compilation artifacts are easy for a developer to overlook and hard to scrub after the fact, and they persist across otherwise unrelated tools. Here, one path was enough to cluster a stealer, a remote-access tool, and a ransomware family under a common developer, and to expose an actively developed, multi-platform malware line. For defenders and threat researchers, those artifacts are a durable pivot for attribution and for finding related samples that no signature would connect.
FAQ
What is an HVNC tool? A “hidden virtual network computing” tool that gives an attacker interactive remote control of a machine in a hidden desktop session, so the activity stays invisible to the person using the computer.
What are AMSI and ETW? Windows interfaces that security products use to inspect scripts and system activity. Malware that tampers with them, as this HVNC sample does, is trying to blind those defenses.
Why does a build path leak matter? Compilation artifacts such as a developer’s home-directory path are often left in binaries unintentionally. Because the same artifact can appear across unrelated tools, it lets researchers link samples, and sometimes a developer, that would otherwise look unconnected.
Indicators of compromise
| Indicator |
Type |
fad8f76afec90c888b4a739539deae250320fd49c34ef8458833b356ea9b7767 |
Zer0day Stealer variant 1, SHA256 |
d0f0734d4e31ec126da43a46896d0cd761e5532c0c385db6226cc5a6927d7722 |
Zer0day Stealer variant 2, SHA256 |
f9964a8d9d01052d9bebe057deadd7ce9d794e8296e2a72229f8ae4aa62ae224 |
Zer0day Dropper (Rust) variant 1, SHA256 |
7cb59abaa268ac66461447773d46bb0b0e5e2568e35e1a8f1d07ac2ec57f67a6 |
Zer0day Dropper (Rust) variant 2, SHA256 |
6bddf59e2a5065255cfc90d2e2e66e3bfd4a7cbf4e0b6341b4da93b574cc4f53 |
Zer0day Dropper (C), SHA256 |
278762dfc0f743216a475919bdc9ecc59735bcc247bba5b7b468fc475407ec6a |
Zer0day HVNC, SHA256 |
178f890f62db90738b11300dd272537240b1c8a599d2ebeccdea01654811fed0 |
HVNC PowerShell, SHA256 |
6aef80514237808dfe25621a8912422d20a8414bc2054008a119e541166821b5 |
PowerShell Dropper, SHA256 |
abd43578b135df61f49844087af0b372ae10b2f27721ad6ba09710760ab0b240 |
ENIGMA Locker, SHA256 |
93.152.220[.]87:5000 |
C2 |
93.152.223[.]30:5555 |
C2 |
Additional network paths and the full analysis are available in the linked report. https://vmray.com/analyses/zer0day-stealer-linked-to-ransomware-via-home-path/report/overview.html