
Imagine you get an SMS promising a tax refund about $3,000 and you tap the link. The page that loads looks almost identical to the tax authority's own website. South Africa's revenue service, SARS, put out a public warning about exactly this kind of lure in late July, citing a R48,900 figure.[1]

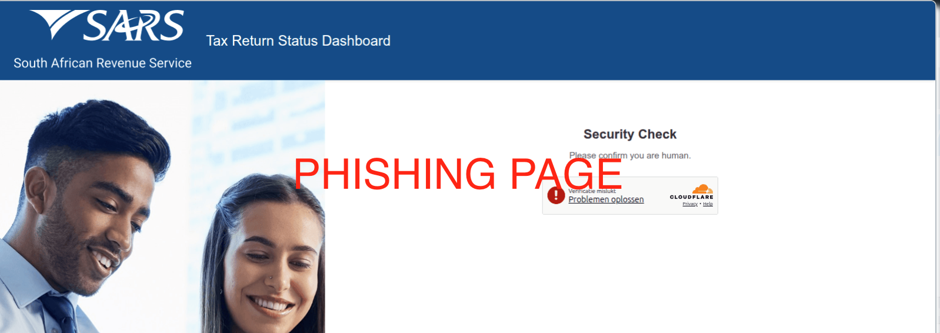
I found the first two sitting quietly in the VMRay UniqueSignal threat feed, then spent an afternoon finding out what they were connected to.
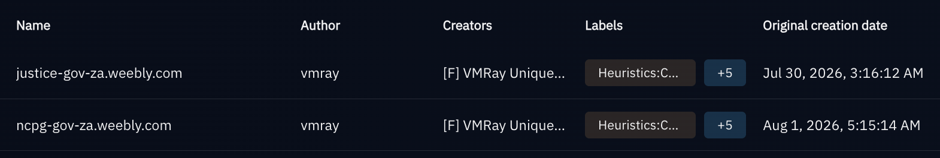
UniqueSignal is VMRay's continuously-updated feed of freshly observed, sandbox-verified indicators. In a typical workflow, an analyst takes one of these indicators and pushes it into a blocklist. This time I will take the same indicator further to see where it leads us.
The two domains (justice-gov-za.weebly[.]com and ncpg-gov-za.weebly[.]com) landed in the UniqueSignal feed. VirusTotal first saw them resolve on July 20th and July 31st respectively.


What I uncovered a few pivots later was a multi-country phishing operation impersonating government agencies, banks, registrars and other organizations around the world.
The investigation in numbers
From two UniqueSignal domains to 50 lures in 11 countries
justice-gov-za.weebly[.]com and ncpg-gov-za.weebly[.]com1,302historical urlscan scans for the *gov-za* naming pattern
372historical urlscan scans on one IP, 46.151.182[.]230 at Ghosty Networks
50lure domains, impersonating organizations in 11 countries
Pivot One: The Naming Convention
Let's search our first two leads on VirusTotal:
justice-gov-za.weebly[.]comncpg-gov-za.weebly[.]com
Both sites point to the same two IP addresses (74.115.51[.]8 and 74.115.51[.]9), which belong to Weebly's shared hosting infrastructure (AS27647). They also sit behind the same wildcard SSL certificate covering *.weebly.com that is shared across every free Weebly site. None of that is pivotable though. Thousands of legitimate Weebly sites share those IPs and that certificate.
The naming convention itself however, turned out to be the one usable fingerprint.
VirusTotal Intelligence: entity:domain and domain:*-gov-za.weebly.com
This pivot added one sibling: 4373-kznhealth-gov-za.weebly[.]com, impersonating KwaZulu-Natal's Department of Health.
As a next step, I dropped .weebly.com from the query entirely to see whether the same naming pattern showed up on other providers. A custom domain would open up new pivoting opportunities that Weebly's shared hosting couldn't offer.
VirusTotal Intelligence: entity:domain and domain:*gov-za*
This returned a much larger and noisier set. I checked each result to see whether the domain served an impersonation page. The Indicators of Compromise table at the bottom lists each domain with the organization it impersonates and the hosting provider. Where the page didn't name the organization it impersonates, the table lists it as unknown.
Pivot Two: Ghosty Networks Hosting
domain:*gov-za* query on URL and website scanner - urlscan.io[2] returned 1,302 historical scans against this naming pattern. Here’s the Urlscan report for one specific SARS lure.
The SARS Example
Examining this result showed the page is titled "Tax Return Status Dashboard - SARS". The page loads an antibot.js script, then a Cloudflare Turnstile challenge before serving content. This antibot + turnstile gate is standard in commercial kits. It hides the lure from scanners and researchers.
The Dead End: Page Title
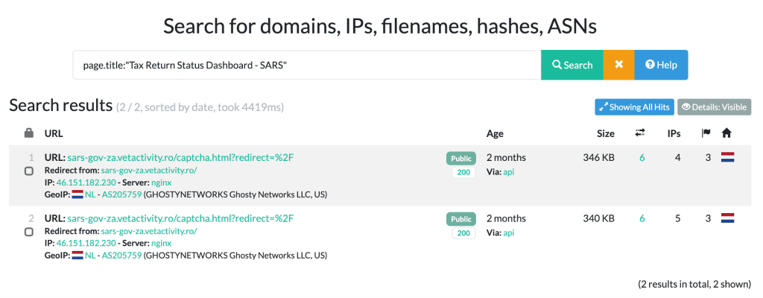
Next, I tried the page title itself as a pivot.[3] Only one domain came back as a result.
Urlscan: page.title:"Tax Return Status Dashboard - SARS"
The Shared IP Address
Coming up empty on the title put me back on the SARS lure's (sars-gov-za.vetactivity[.]ro) own infrastructure. The domain resolves to 46.151.182[.]230 which belongs to Ghosty Networks LLC (AS205759). Intrinsec classifies Ghosty Networks as a bulletproof network, citing its use in March 2026 malspam campaigns and its likely links to Optibounce and AnonRDP.[4] That's worth pivoting on. So I ran page.ip:46.151.182.230 on Urlscan.[5] It came back with 372 historical scans.

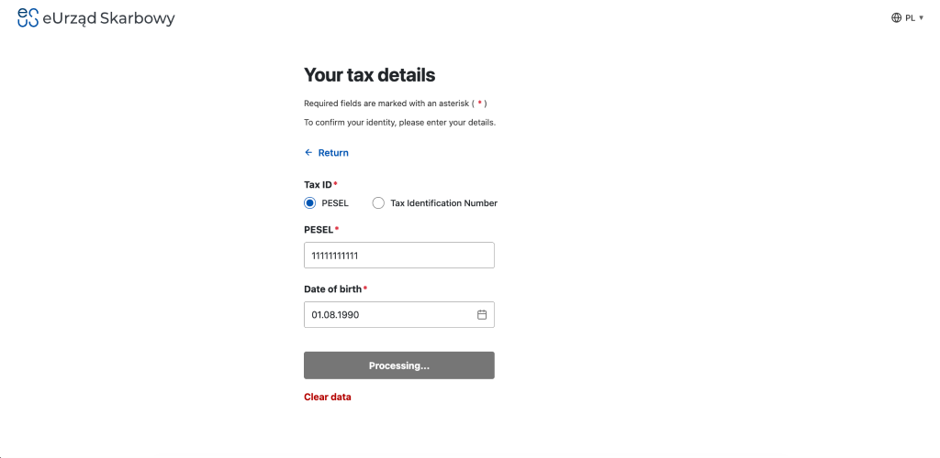
This query turned up six instances of a Polish tax-authority lure all titled "e-Urząd Skarbowy - Twoje dane podatkowe" and run through the identical captcha.html/antibot flow as the SARS page.
etax.vetactivity[.]roetaxpanel.vetactivity[.]roetax.clinicaactmedica[.]roetaxpanel.clinicaactmedica[.]roetax.onestaprod[.]roetex-poland.energy-report[.]ro
| Artifact | Value |
|---|---|
| Bot-check file | captcha.html |
| File hash (antibot.js) | 095b95643a6c7ddbe2a70bd28e00556e2c2bf9b4eb83df93074d80fc1c9b60c0 |
Note: Because Cloudflare ties each Turnstile sitekey to a single account, the same sitekey showing up across multiple domains is a strong signal they belong to the same operator, even when the sitekey itself can't be used as a search pivot.
To tell which domains the attacker owns outright versus which they've compromised, compare passive DNS history at the apex against the subdomain. A compromised domain shows years of stable apex history that only diverges recently, while the apex keeps resolving elsewhere. An attacker-owned domain has no such split. The Ownership column in the Indicators of Compromise table applies this test to every domain.
Pivoting this IP directly shows dedicated infrastructure that hosted numerous phishing kit deployments. SARS is a South African entry in a cluster that already covers multiple countries' tax authorities, banks and registrars.
| Brand | Country | Sector | Host | WHOIS | First pDNS |
|---|---|---|---|---|---|
| Crédit Agricole | France | Banking | ca24-credit-agricole.vetactivity[.]ro | 2021-10-02 | 2026-07-23 |
| Íslandsbanki | Iceland | Banking | islanbsdanki.clinicaactmedica[.]ro | 2014-11-11 | 2026-06-27 |
| cdmon | Spain | Domain registrar | cdmon.hahn-polyfilms[.]com | 2005-04-29 | 2026-08-13 |
| Verification | Belarus | Hosting panel | hoster-by[.]org | 2026-07-13 | 2026-07-13 |
| Vautron | Germany | Domain registrar | vautron.vetactivity[.]ro | 2021-10-02 | 2026-08-06 |
| Webhostone | Germany | Hosting/registrar | webhostone-de.vetactivity[.]ro | 2021-10-02 | 2026-08-17 |
| 1984 Hosting | Iceland | Hosting/registrar | 1984-hosting.vetactivity[.]ro | 2021-10-02 | 2026-08-18 |
| Skatturinn (RSK) | Iceland | Tax authority | skatturinn.onestaprod[.]ro | 2013-02-19 | 2026-09-04 |
| VMI | Lithuania | Tax authority | vmi.onestaprod[.]ro | 2013-02-19 | 2026-09-04 |
| e& enterprise | UAE | Telecom | nic-ae.energy-report[.]ro | 2017-04-28 | 2026-08-27 |
| OpenAI | USA | Software | checkout-openai-llc.onestaprod[.]ro | 2013-02-19 | 2026-09-09 |
The full timeline
Each dot is one domain’s earliest passive DNS record, on the row of the country it impersonates.
Seed domains from UniqueSignalLast five months
What This Means for Defenders
Two Weebly URLs in the UniqueSignal feed turned into a number of government lures. One of those lures led to something bigger. One IP hosting the same kit under multiple countries' brands.
The following detection actions are advised:
- Block
46.151.182[.]230and watch AS205759 for new hosting of the kit. - Hunt for the
captcha.htmlpath with theantibot.jshash in urlscan and in proxy logs that record file hashes. The SARS and Polish tax lures share this flow. - Monitor new
*-gov-zadomains, including*.weebly.comand*.pages.devsubdomains. On shared platforms the name is the only selective fingerprint.

MITRE ATT&CK Mapping
| Tactic | Technique | Where it shows up |
|---|---|---|
| Resource Development | T1583.001 Acquire Infrastructure: Domains | Look-alike *-gov-za domains, plus attacker-registered brand domains such as hoster-by[.]org |
| Resource Development | T1583.003 Acquire Infrastructure: Virtual Private Server | Dedicated kit server at 46.151.182[.]230 (Ghosty Networks, AS205759) |
| Resource Development | T1583.006 Acquire Infrastructure: Web Services | Weebly and Cloudflare Pages lures |
| Resource Development | T1584.001 Compromise Infrastructure: Domains | vetactivity[.]ro, onestaprod[.]ro, clinicaactmedica[.]ro, energy-report[.]ro, hahn-polyfilms[.]com, aniamis[.]ro and koeller-solutions[.]de (assessed from pDNS, not confirmed) |
| Initial Access | T1566.002 Phishing: Spearphishing Link | SMS and email lures (per SARS's public alert, not observed directly) |
| Defense Evasion | T1656 Impersonation | Government, bank and registrar brand clones |
| Defense Evasion | T1497 Virtualization/Sandbox Evasion | antibot.js and Cloudflare Turnstile gate (closest fit for bot evasion) |
| Reconnaissance | T1598.003 Phishing for Information: Spearphishing Link | Credential and card harvesting pages |
Indicators of Compromise
First seen is the date of the earliest VirusTotal passive DNS record for the domain. It shows when VirusTotal first saw the domain resolve, so the lure may have been live earlier.
| First seen | Indicator | Imp. Country | Impersonates | Hosting provider | Ownership (pDNS) |
|---|---|---|---|---|---|
| - | 46.151.182[.]230 | - | - | Ghosty Networks | Shared |
| - | antibot.js hash (SHA-256): 095b95643a6c7ddbe2a70bd28e00556e2c2bf9b4eb83df93074d80fc1c9b60c0 | - | - | - | - |
| 2025-05-21 | 4373-kznhealth-gov-za.weebly[.]com | South Africa | KZN Dept. of Health | Weebly | Free platform |
| 2025-07-11 | www-saps-gov-za-careers.pages[.]dev | South Africa | SAPS careers portal | Cloudflare | Free platform |
| 2025-07-15 | erecruitmentincidents-saps-gov-za.pages[.]dev | South Africa | SAPS recruitment | Cloudflare | Free platform |
| 2025-07-17 | sars-gov-za.pages[.]dev | South Africa | South African Revenue Service | Cloudflare | Free platform |
| 2025-08-02 | dalrrd-gov-za.pages[.]dev | South Africa | Dept. of Agriculture, Land Reform | Cloudflare | Free platform |
| 2025-08-05 | natis-gov-za[.]org | South Africa | NATIS (licence/fines) | Oracle, then Amazon | Attacker-owned |
| 2025-08-06 | natis-gov-za[.]com | South Africa | NATIS (licence/fines) | Oracle, then Amazon | Attacker-owned |
| 2025-08-15 | emadlangeni-gov-za.pages[.]dev | South Africa | eMadlangeni local municipality | Cloudflare | Free platform |
| 2025-09-03 | education-fs-gov-za.pages[.]dev | South Africa | Free State Dept. of Education | Cloudflare | Free platform |
| 2026-01-03 | track.mail.dws-gov-za[.]co | South Africa | Dept. of Water & Sanitation | Amazon | Attacker-owned |
| 2026-01-12 | dot-gov-za[.]bid | South Africa | Dept. of Transport | Contabo | Attacker-owned |
| 2026-04-05 | www-intsikayethu-gov-za.pages[.]dev | South Africa | Intsika Yethu local municipality | Cloudflare | Free platform |
| 2026-04-15 | smade.aniamis[.]ro | unknown | unknown | Maroc Telecom, then Ghosty Networks | Compromised |
| 2026-04-17 | track.mail.dot-gov-za[.]bid | South Africa | Dept. of Transport | Cloudflare | Attacker-owned |
| 2026-05-19 | kgetlengrivier-gov-za.pages[.]dev | South Africa | Kgetlengrivier local municipality | Cloudflare | Free platform |
| 2026-06-16 | dcs-gov-za[.]org | South Africa | Dept. of Correctional Services | Amazon | Attacker-owned |
| 2026-06-17 | chat.clinicaactmedica[.]ro | unknown | unknown | Ghosty Networks | Compromised |
| 2026-06-19 | etax.clinicaactmedica[.]ro | Poland | e-Urząd Skarbowy (Polish tax authority) | Ghosty Networks, then Cyber_Folks | Compromised |
| 2026-06-27 | islanbsdanki.clinicaactmedica[.]ro | Iceland | Íslandsbanki (Icelandic bank) | Ghosty Networks | Compromised |
| 2026-07-09 | etaxpanel.clinicaactmedica[.]ro | Poland | e-Urząd Skarbowy (Polish tax authority) | Ghosty Networks, then Cyber_Folks | Compromised |
| 2026-07-10 | etaxpanel.vetactivity[.]ro | Poland | e-Urząd Skarbowy (Polish tax authority) | Ghosty Networks | Compromised |
| 2026-07-13 | hoster-by[.]org | Belarus | Verification (hosting panel) | Ghosty Networks | Attacker-owned |
| 2026-07-20 | justice-gov-za.weebly[.]com | South Africa | Dept. of Justice | Weebly | Free platform |
| 2026-07-23 | ca24-credit-agricole.vetactivity[.]ro | France | Crédit Agricole (bank) | Ghosty Networks | Compromised |
| 2026-07-30 | hoster.vetactivity[.]ro | Kazakhstan | ᐈ Купить хостинг в Казахстане. Регистрация доменов .KZ (hosting panel) | Ghosty Networks | Compromised |
| 2026-07-31 | ncpg-gov-za.weebly[.]com | South Africa | National Council on Problem Gambling | Weebly | Free platform |
| 2026-08-03 | etax.vetactivity[.]ro | Poland | e-Urząd Skarbowy (Polish tax authority) | Ghosty Networks | Compromised |
| 2026-08-04 | elester.vetactivity[.]ro | Germany | ELSTER (German tax portal) | Ghosty Networks | Compromised |
| 2026-08-04 | interdominios.vetactivity[.]ro | Spain | Interdominios (Spanish registrar) | Ghosty Networks | Compromised |
| 2026-08-06 | vautron.vetactivity[.]ro | Germany | Vautron (German registrar) | Ghosty Networks | Compromised |
| 2026-08-07 | sportsplus-gov-za[.]ph | South Africa | Sport body | Akamai | Attacker-owned |
| 2026-08-08 | sars-gov-za.vetactivity[.]ro | South Africa | South African Revenue Service | Ghosty Networks | Compromised |
| 2026-08-08 | www.sars-gov-za.vetactivity[.]ro | South Africa | South African Revenue Service | Ghosty Networks | Compromised |
| 2026-08-11 | natis-gov-za.centroayuda[.]es | South Africa | NATIS (licence/fines) | Team Internet | Attacker-owned |
| 2026-08-12 | bma-gov-za-alexistoto.pages[.]dev | South Africa | Border Management Authority | Cloudflare | Free platform |
| 2026-08-13 | cdmon.hahn-polyfilms[.]com | Spain | cdmon (Spanish registrar) | Ghosty Networks | Compromised |
| 2026-08-17 | webhostone-de.vetactivity[.]ro | Germany | Webhostone (German hosting/registrar) | Ghosty Networks | Compromised |
| 2026-08-18 | 1984-hosting.vetactivity[.]ro | Iceland | 1984 Hosting (Icelandic hosting/registrar) | Ghosty Networks | Compromised |
| 2026-08-24 | etex-poland.energy-report[.]ro | Poland | e-Urząd Skarbowy (Polish tax authority) | ᐈ Купить хостинг в Казахстане. Регистрация доменов .KZ, then Ghosty Networks | Compromised |
| 2026-08-27 | nic-ae.energy-report[.]ro | UAE | e& enterprise (UAE telecom) | Ghosty Networks | Compromised |
| 2026-09-01 | account.energy-report[.]ro | unknown | unknown | Ghosty Networks | Compromised |
| 2026-09-02 | secure-vmi.energy-report[.]ro | Lithuania | VMI (Lithuanian tax authority) | Ghosty Networks | Compromised |
| 2026-09-02 | login-taw.energy-report[.]ro | unknown | unknown | Ghosty Networks | Compromised |
| 2026-09-02 | intoz.koeller-solutions[.]de | Germany | Koeller Solutions (company brand) | Ghosty Networks | Compromised |
| 2026-09-04 | skatturinn.onestaprod[.]ro | Iceland | Skatturinn / RSK (Icelandic tax authority) | Ghosty Networks | Compromised |
| 2026-09-04 | vmi.onestaprod[.]ro | Lithuania | VMI (Lithuanian tax authority) | Ghosty Networks | Compromised |
| 2026-09-05 | refund.onestaprod[.]ro | unknown | unknown | Ghosty Networks | Compromised |
| 2026-09-08 | etax.onestaprod[.]ro | Poland | e-Urząd Skarbowy (Polish tax authority) | Ghosty Networks | Compromised |
| 2026-09-09 | checkout-openai-llc.onestaprod[.]ro | USA | OpenAI (checkout / card theft) | Cyber_Folks, then Ghosty Networks | Compromised |
| 2026-09-10 | linkguard.onestaprod[.]ro | Iceland | Skatturinn / RSK (Icelandic tax authority) | Ghosty Networks | Compromised |
- [1] Scam alert - 'Tax Return Notification' | South African Revenue Service
- [2] Search - urlscan.io
- [3] Search - urlscan.io
- [4] Pivoting on a malspam infrastructure delivering JS malware backed by bulletproof networks
- [5] Search - urlscan.io
Frequently asked questions
What did this research find?
Two phishing domains from the VMRay UniqueSignal feed, both impersonating South African government bodies on Weebly, led to a dedicated server at 46.151.182[.]230 on Ghosty Networks (AS205759). That server hosted the same phishing kit under the brands of tax authorities, banks, registrars and other organizations in multiple countries, from South Africa and Poland to Iceland, Germany and the UAE.
How did the investigation move from two domains to the wider operation?
In three pivots. The shared *-gov-za naming convention surfaced more South African lures on Weebly, Cloudflare Pages and custom domains. A urlscan search on that pattern led to a SARS lure hosted on 46.151.182[.]230. Searching that IP returned 372 historical scans, including the Polish tax-authority lures and the other brands in the Indicators of Compromise table.
Why is the domain name the only usable fingerprint on Weebly and Cloudflare Pages?
Free sites on these platforms share IP addresses and a wildcard SSL certificate with thousands of legitimate sites, so neither identifies the operator. The naming pattern, such as *-gov-za, is the one selective signal.
How does the kit hide its pages from scanners?
The lure pages load an antibot.js script and then a Cloudflare Turnstile challenge, served through a captcha.html page, before showing any content. The SARS and Polish tax lures use the identical flow.
How can you tell a compromised domain from one the attacker registered?
Compare passive DNS history at the apex domain with the subdomain. A compromised domain shows years of stable apex history and only the subdomain diverges recently. An attacker-owned domain has no such split.
What should defenders do?
Block 46.151.182[.]230 and watch AS205759 for new hosting of the kit. Hunt for the captcha.html path with the antibot.js hash (SHA-256 095b95643a6c7ddbe2a70bd28e00556e2c2bf9b4eb83df93074d80fc1c9b60c0) in urlscan and in proxy logs. Monitor new *-gov-za domains, including subdomains on *.weebly.com and *.pages.dev.
Written by
Robin Dimyanoglu
External Threat Researcher / Platform Security Engineer
Robin Dimyanoglu is a Platform Security Engineer with over eight years of experience in Penetration Testing, DevSecOps, Cyber Threat Intelligence, Malware Reverse Engineering, and instructing. Robin is an active member of the cyber security community and has participated in multiple conferences as a speaker, particularly on his research related to Early Warning Intelligence and Predictive Cyber Defense. He actively develops and publishes methodologies on PredictiveDefense.io and is the author of the book Geopolitical Cyber Threat Intelligence. Robin previously worked at several consultancy firms, delivering threat intelligence to leading clients by reverse engineering Windows/PE and Linux/ELF binaries using tools like IDA Pro, WinDbg, Sysinternals, Rekall, and Fakenet. He also delivered hands-on training for SOC teams focused on reverse engineering and malware analysis.