Category: Malware Analysis

2017-04-20

Undetected JScript Dropper Installs Sage Ransomware

A popular method to distribute malware (especially ransomware) is to send a

[Video] Analyzing a Malicious Microsoft Word Document

One of the key features in VMRay Analyzer 2.0 is the built-in

Analyzing Malware Embedded in MS Publisher Files

We have started to see malware authors use embedded Visual Basic (VBA)
2017-01-17

Spora Ransomware Dropper Uses HTA to Infect System

This past week, a new Ransomware variant called Spora was spotted in
2016-12-14

AtomBombing Evasion and Detection

A new code injection technique is effective in bypassing most analysis and
2016-12-08

Goldeneye Ransomware Uses COM to Execute Malicious JavaScript

There is a new ransomware going wild in Germany called Goldeneye, which
2016-12-08

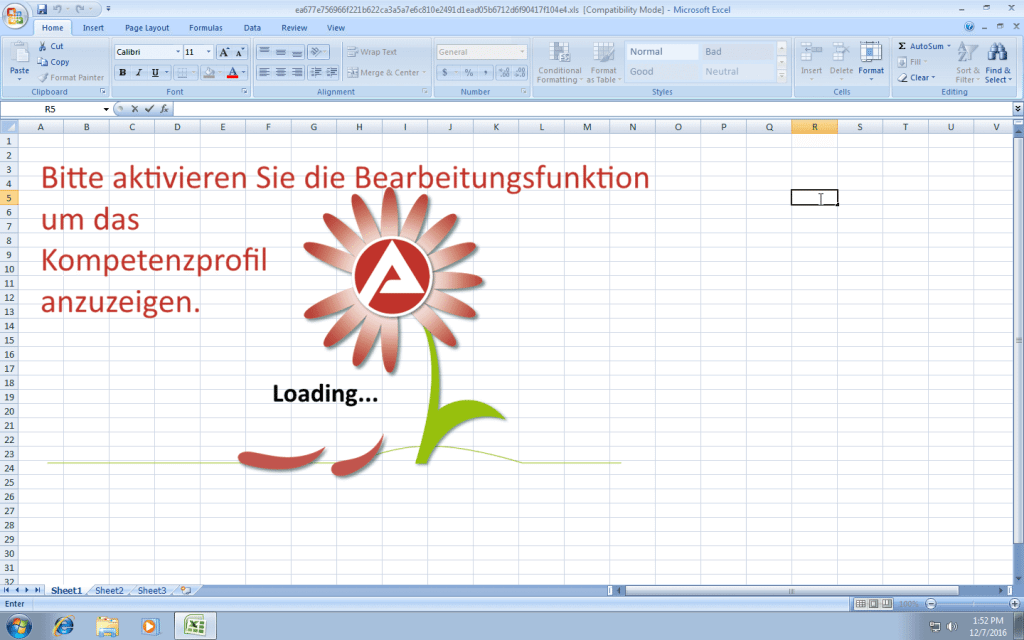
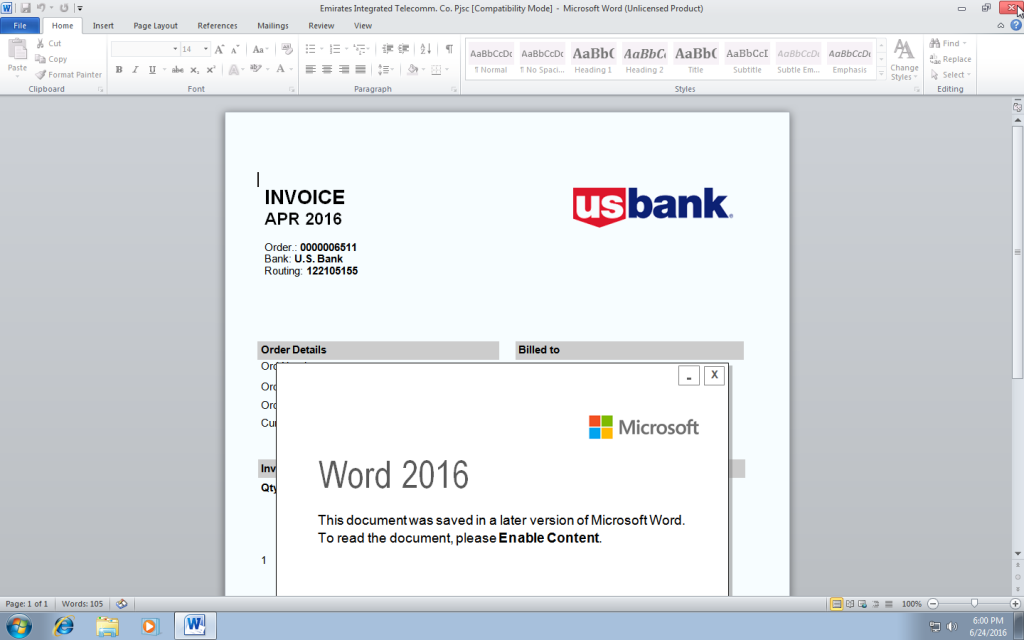
Hancitor Uses Microsoft Word to Deliver Malware

There have been several variants of the Hancitor malware family seen in

Word macro uses WMI to detect VM environments

We recently came across an interesting malicious Word document that used an

Powershell Ransomware – a PowerWare Deep Dive

Malware authors are always looking for an edge to evade detection and

Eliminating the Observer Effect in Malware Analysis

We have a mission at VMRay to build the ultimate malware Panopticon

Uncover the truth of Cybersecurity, one story at a time

Keep up to date with our weekly digest of articles. Get the latest news, invites to events, and threat alerts!

Subscribe to our Newsletter