
VMRay is a Microsoft Intelligent Security Association (MISA) member. Our integrations with Microsoft Defender for Endpoint, Microsoft Defender for Office, and Microsoft Sentinel turn each alert into a verdict your SOC can act on, and push the IOCs back into your Microsoft Security stack to block what comes next.
 It spans the full content width; logos are centered and never cropped. -->
The era of the single malicious link is fading. What's landing in SOC queues today is multi-stage delivery chains designed to slip past automated defenses, and only reveal their intent three layers in.
Clean-looking emails carrying password-protected documents. PDFs with embedded QR codes. Redirects through legitimate services. ClickFix payloads that surface only after a series of interactions across multiple layers.
Microsoft Security catches the alert. The question for your team is the one that comes next: what is this, what would it have done, and can the verdict be trusted enough to move on?
 as the FIRST child inside the .visual-slot below. It covers the built-in
diagram and fills the frame. Leave it out to keep the built-in diagram. -->

Inside the Microsoft console, and ready when your team needs to go deeper. Three things that change when VMRay's analysis sits behind the alert.
Malicious or not, the malware family, the threat classifications, and the top behaviors observed during detonation. A junior analyst reads it in seconds. An automated playbook acts on it without manual re-checks.
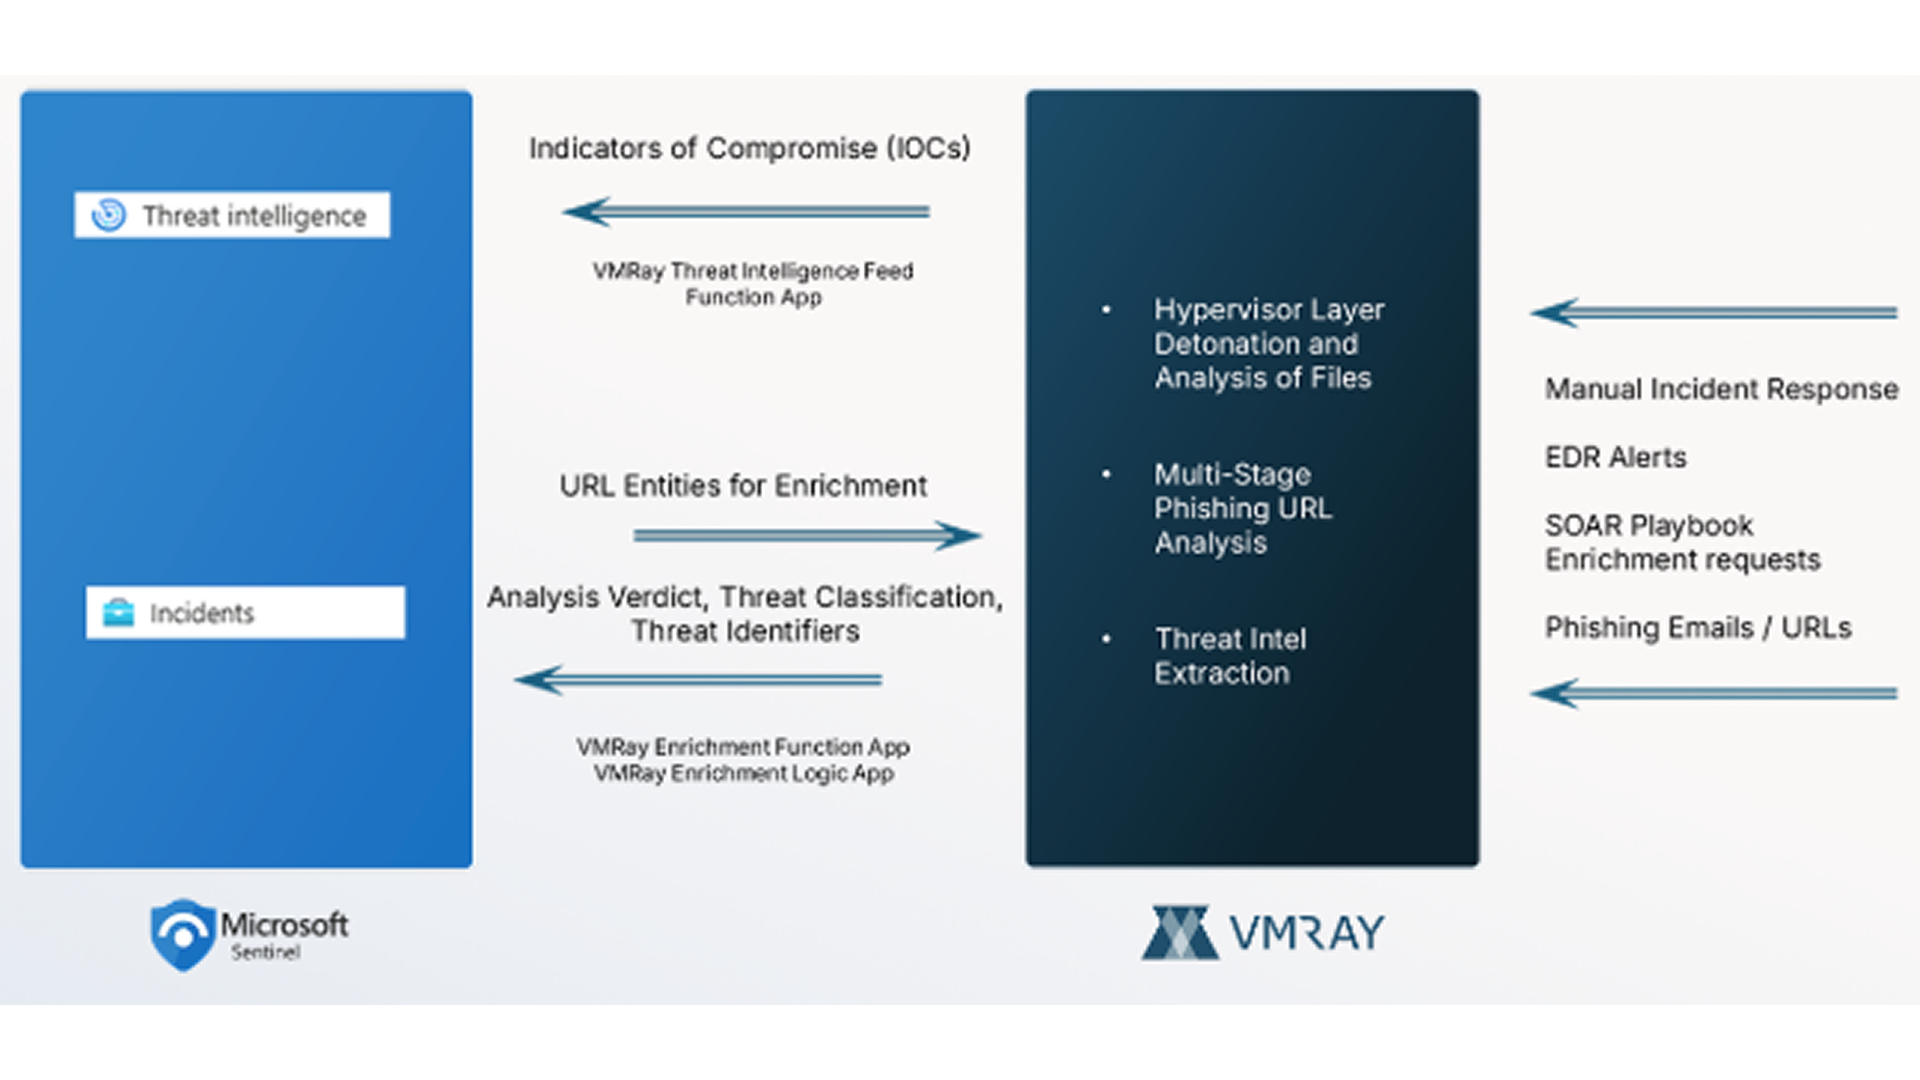
// MICROSOFT DEFENDERThe high-fidelity indicators extracted during analysis flow straight into Microsoft Defender indicators and Sentinel Threat Intelligence. No manual import. No copy-paste between consoles.
// MICROSOFT DEFENDER + SENTINELWhen an alert turns into an investigation, the complete VMRay analysis is linked from the comment: full delivery chain, extracted malware configuration, MITRE ATT&CK TTPs, network traffic, and more.
// VMRAY PLATFORMSets the disposition of the alert in a single read.
What it is, and why we think it's malicious.
Malware configuration, ATT&CK mapping, network traffic, and more.
Three integrations with Microsoft's primary security tools, each built on the same evasion-resistant analysis engine. Pick the one closest to where you're working.
Quarantined files and suspicious URLs from Defender alerts go through VMRay, automatically. The verdict, threat name, and top VTIs appear in the alert comment. IOCs are pushed to Defender indicators and block lists. The full recursive analysis is one click away.
Quarantined files & URLs analyzed in the background
IOCs flow directly to Defender block lists
Full attack chain, beyond what EDR sees
Minimal setup, native deployment

Microsoft Defender for Office protects email at scale. VMRay adds depth where it matters most: in the User Reported Phishing folder, where the novel, evasive attacks tend to land. URLs and attachments are detonated automatically. QR codes are decoded and followed. Password-protected files are opened. ClickFix payloads are captured.
Gain full visibility into each stage of an attack
Get instant clarity on Microsoft alerts
Automatically add IOCs to prevent future attacks
In-depth reports to speed up investigation

Every IOC produced by VMRay analysis flows directly into Sentinel Threat Intelligence, building a curated intelligence layer from threats already seen in your environment. The VMRay UniqueSignal feed is ingested via STIX/TAXII alongside it. Two complementary intelligence sources, ready for correlation and automation.
Sentinel-detected URLs automatically tagged with verdicts
VMRay's curated CTI feed, via STIX/TAXII
Analysis results added to your TI repository
Clean, filtered indicators for playbooks
Security automation is only useful if the analysis layer feeding it can be trusted. Here's what makes VMRay's verdicts reliable enough to drive automation across your Microsoft Security stack.
VMRay's analysis runs in a hypervisor-based analysis environment, operating below the OS where malware cannot detect it. No agents visible to the sample. That's the foundation that makes the verdicts feeding your Microsoft Defender and Microsoft Sentinel reliable enough to automate on.
And it's the same foundation that makes the IOCs trustworthy: because the behavior they describe is what the malware actually did, not what it was prepared to show to a sandbox.
VMRay is a Microsoft Intelligent Security Association (MISA) member. Our integrations are production-deployed across the most demanding security operations in the world.
VMRay emerged as our go-to platform for validating alerts from CrowdStrike and MS Defender for Endpoints. Its ability to uncover hidden threats that eluded other tools in our security stack gave us confidence in our security posture and saved us valuable time in incident response.